Adversaries with the deepest capabilities
Defense systems face the most capable attackers in the world. The servers behind mission systems carry a power layer below the operating system, the part few tools watch.
 PowerGuardBAREKET AIRequest a pilot
PowerGuard brings security to the power layer of defense infrastructure, the control chips beneath every server in your data centers and mission systems, the layer most security tools cannot see. Running as software on the fleet you already have, it maps the power chips across every site, watches how they behave in real time, and gives each event a clear verdict: normal, suspicious or attack.
Request a pilotDefense organizations and the industrial base behind them run mission-critical systems on fleets of servers, under constant pressure from the most capable adversaries. Every one of those servers relies on power control chips, managed through the BMC, that sit below the operating system and outside the view of most security tools. That makes the power layer a growing target for a sector where hardware integrity is mission integrity: state actors reach systems through the supply chain, attackers exploit server management chips, and idle compute is hijacked for hidden crypto mining. PowerGuard brings visibility and fast detection to this layer, running as software on the fleet you already have and sending clear verdicts into the SOC tools you already use.
Defense systems face the most capable attackers in the world. The servers behind mission systems carry a power layer below the operating system, the part few tools watch.
Attackers already exploit server management chips, and researchers have shown that one command through them can bend a server's power to disrupt service or damage hardware.
Idle capacity across defense data centers is a quiet target for crypto miners that hide from monitoring tools. The power they draw is harder to hide.
Finds the power chips on the servers you already run.
Watches them nonstop and gives every event a verdict.
Verdicts flow into Splunk or Datadog, and your own controls act on them.
Every verdict is recorded and summarized in regular reports your team can use as evidence for CMMC, NIST 800-171 and internal audits across your estate.
PowerGuard deploys as software across the existing fleet, from one site to thousands, with no new chips and no board redesign.
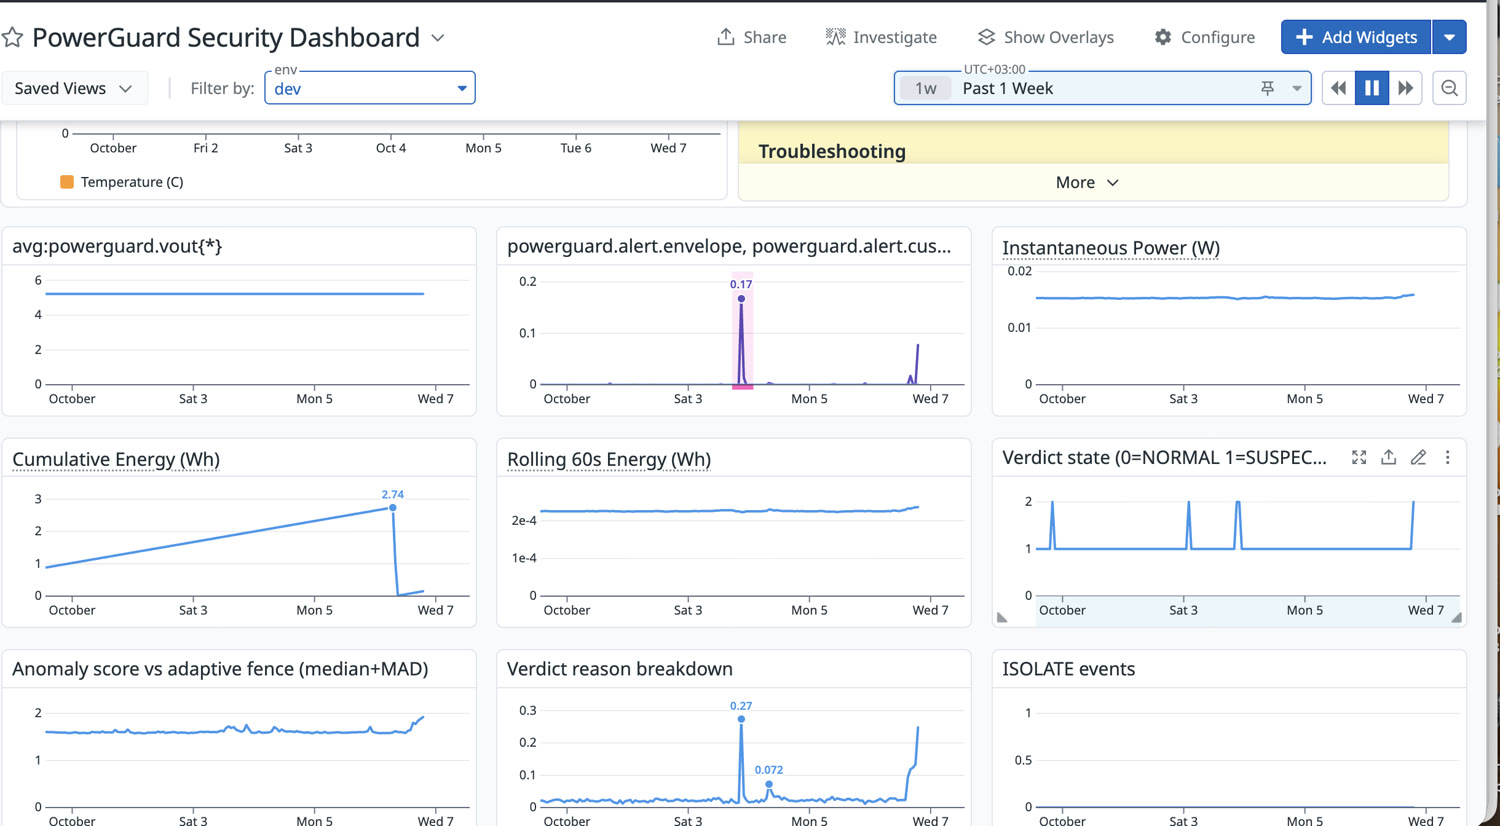
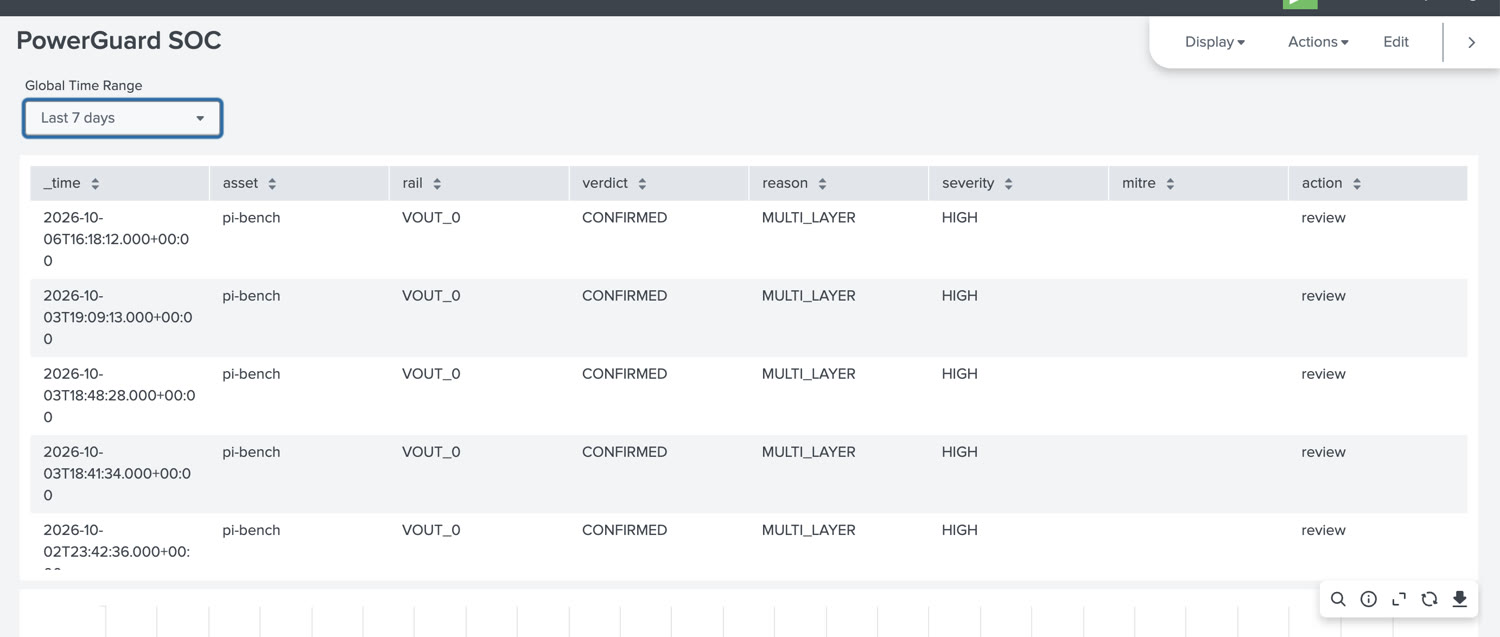
Not a mockup. A live voltage attack pulled a rail from 5.21 V to 4.64 V and was detected in about 20 ms, streamed into Datadog and Splunk, the same tools your team already lives in.
The CMMC program rule sets cybersecurity maturity requirements that contractors across the defense industrial base must meet.
Read moreNIST · SP 800-171NIST SP 800-171 defines the controls that protect controlled unclassified information in nonfederal systems, the baseline for defense suppliers.
Read moreCISA · JUNE 2025A server management chip flaw (CVE-2024-54085) was added to CISA's Known Exploited Vulnerabilities catalog.
Read moreAWS SECURITY BLOG · NOV 2025A cryptomining campaign deployed miners on Amazon EC2 and ECS within ten minutes of gaining access.
Read more