Discover
A live map of the attack surface: every power controller and the hardware it feeds.
Explore the attack surface PowerGuardBAREKET AIRequest a pilot
A compromised administrator or firmware component can issue commands beneath SIEM and EDR visibility. PowerGuard continuously maps this hidden layer, establishes a physical baseline and detects destructive behavior before hardware is damaged.
A live map of the attack surface: every power controller and the hardware it feeds.
Explore the attack surfacePowerGuard watches the power nonstop and tells normal AI load from protocol abuse and destructive commands.
Explore detectionVerdicts carry physical or protocol evidence into your existing controls, never a statistical anomaly alone.
Explore enforcementEvery power controller mapped as attack surface, rails sampled continuously at 100 Hz
AUDIT & COMPLIANCEMeasured against NIS2 and IEC 62443, with evidence packs on demand
PREDICTIVE HEALTHDegrading power hardware surfaced before it takes a server down
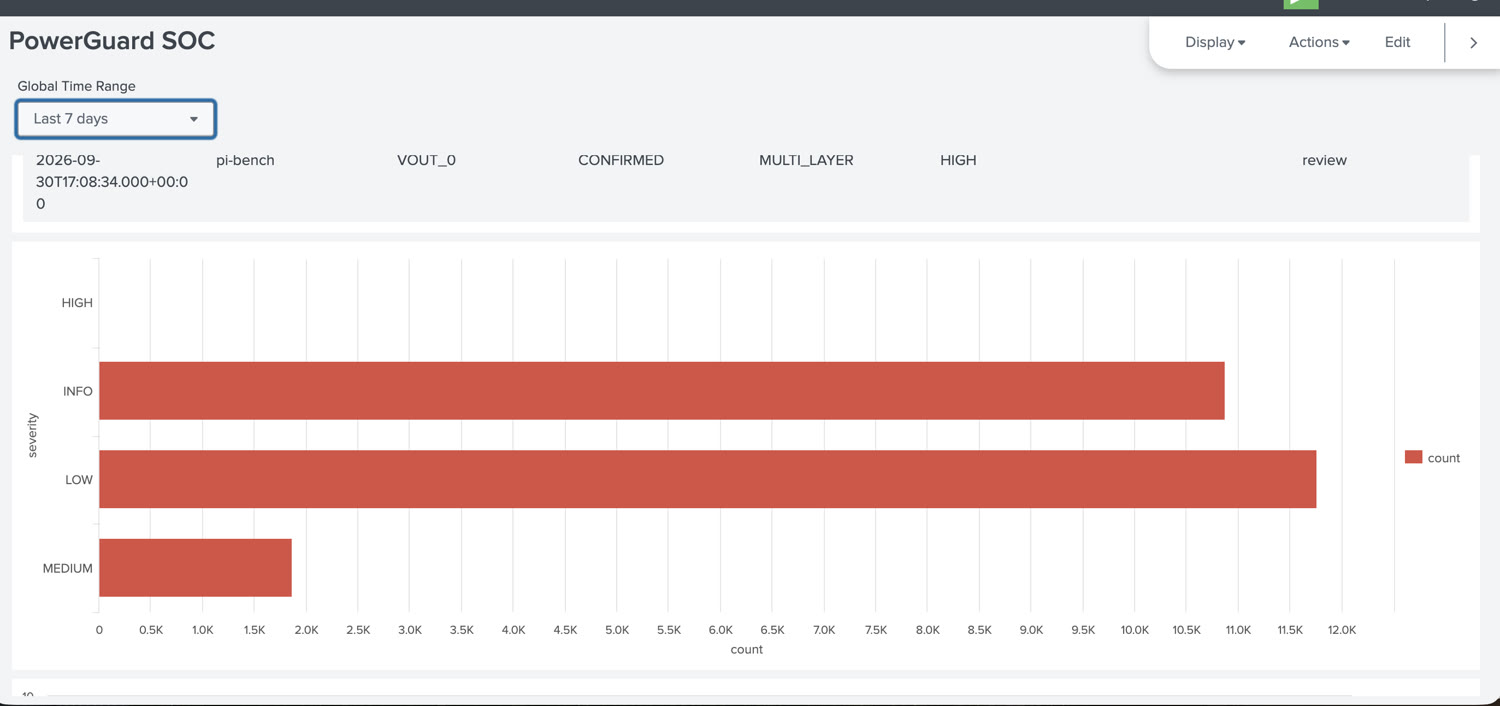
ECOSYSTEM INTEGRATIONSFindings delivered into Splunk, Sentinel, Datadog, ServiceNow, the tools you already run
ACTIVE ENFORCEMENTEvery power command measured against policy, with the verdict carried into the controls you already run
An attacker who reaches the power layer can damage silicon permanently, and nothing above it will record how. PowerGuard holds a physical baseline of your hardware and acts on physical evidence, not on a statistical guess.
The same measurements show hardware degrading before it fails. Power components drift for hours or days before they take a server down.
Early-warning capability is being validated with design partners on production hardware.
Attacks beneath EDR don't write logs. I need evidence, not a guess.Physical evidence in 20 ms.
Ten thousand alerts a day. I need the three that matter.Findings, not firehose.
Not one dollar of new hardware.Nothing installed to start. No new silicon.
You cannot audit a component by asking it how it is doing.
Every server in your estate contains a management controller running firmware you did not write and cannot inspect. It has authority over the physical power of the machine. PowerGuard gives you an independent view of what that layer is actually doing, and a switch that belongs to you.
Every controller ships with code authored under someone else's jurisdiction
We observe the power layer rather than trusting what it reports about itself
Runs fully inside your environment, including disconnected networks
No workload content, no customer data, ever
Enforcement acts under policy you set and can revoke
Designed for defence, government and national infrastructure environments.
On sovereignty and enforcement leverage · Stefan Fritz →
Findings delivered into the tools you already run, see the live Datadog stream on Proof.
The power layer is inside the scope of the major OT and infrastructure frameworks, and today it is the part of the estate with the least evidence behind it. PowerGuard is designed to produce that evidence, on demand.
| FRAMEWORK | OBLIGATION AREA | WHAT POWERGUARD PRODUCES |
|---|---|---|
| NIS2EU 2022/2555 · ART. 21 | Risk-management measures: asset visibility, incident detection and handling, evidence for reporting | Continuous inventory of the power layer; detection with a physical evidence trail; an incident record that survives the incident |
| IEC 62443INDUSTRIAL AUTOMATION & CONTROL | Continuous monitoring and asset inventory of control systems | Per-controller monitoring against a baseline learned from your own hardware; evidence packs on demand |
| NERC CIPBULK ELECTRIC SYSTEM | System security management and internal network security monitoring for cyber systems | Behavioural monitoring of the management plane; alerting into your existing tools; retained records under your control |
POWERGUARD PRODUCES EVIDENCE. COMPLIANCE ITSELF REMAINS AN ASSESSMENT OF YOUR WHOLE ENVIRONMENT · NO SINGLE PRODUCT MAKES YOU COMPLIANT, AND WE DO NOT CLAIM OTHERWISE.